> For the complete documentation index, see [llms.txt](https://intuitem.gitbook.io/ciso-assistant/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://intuitem.gitbook.io/ciso-assistant/configuration/sso/oidc.md).
# OpenID Connect (OIDC)
### Configure CISO Assistant with OpenID Connect (OIDC)
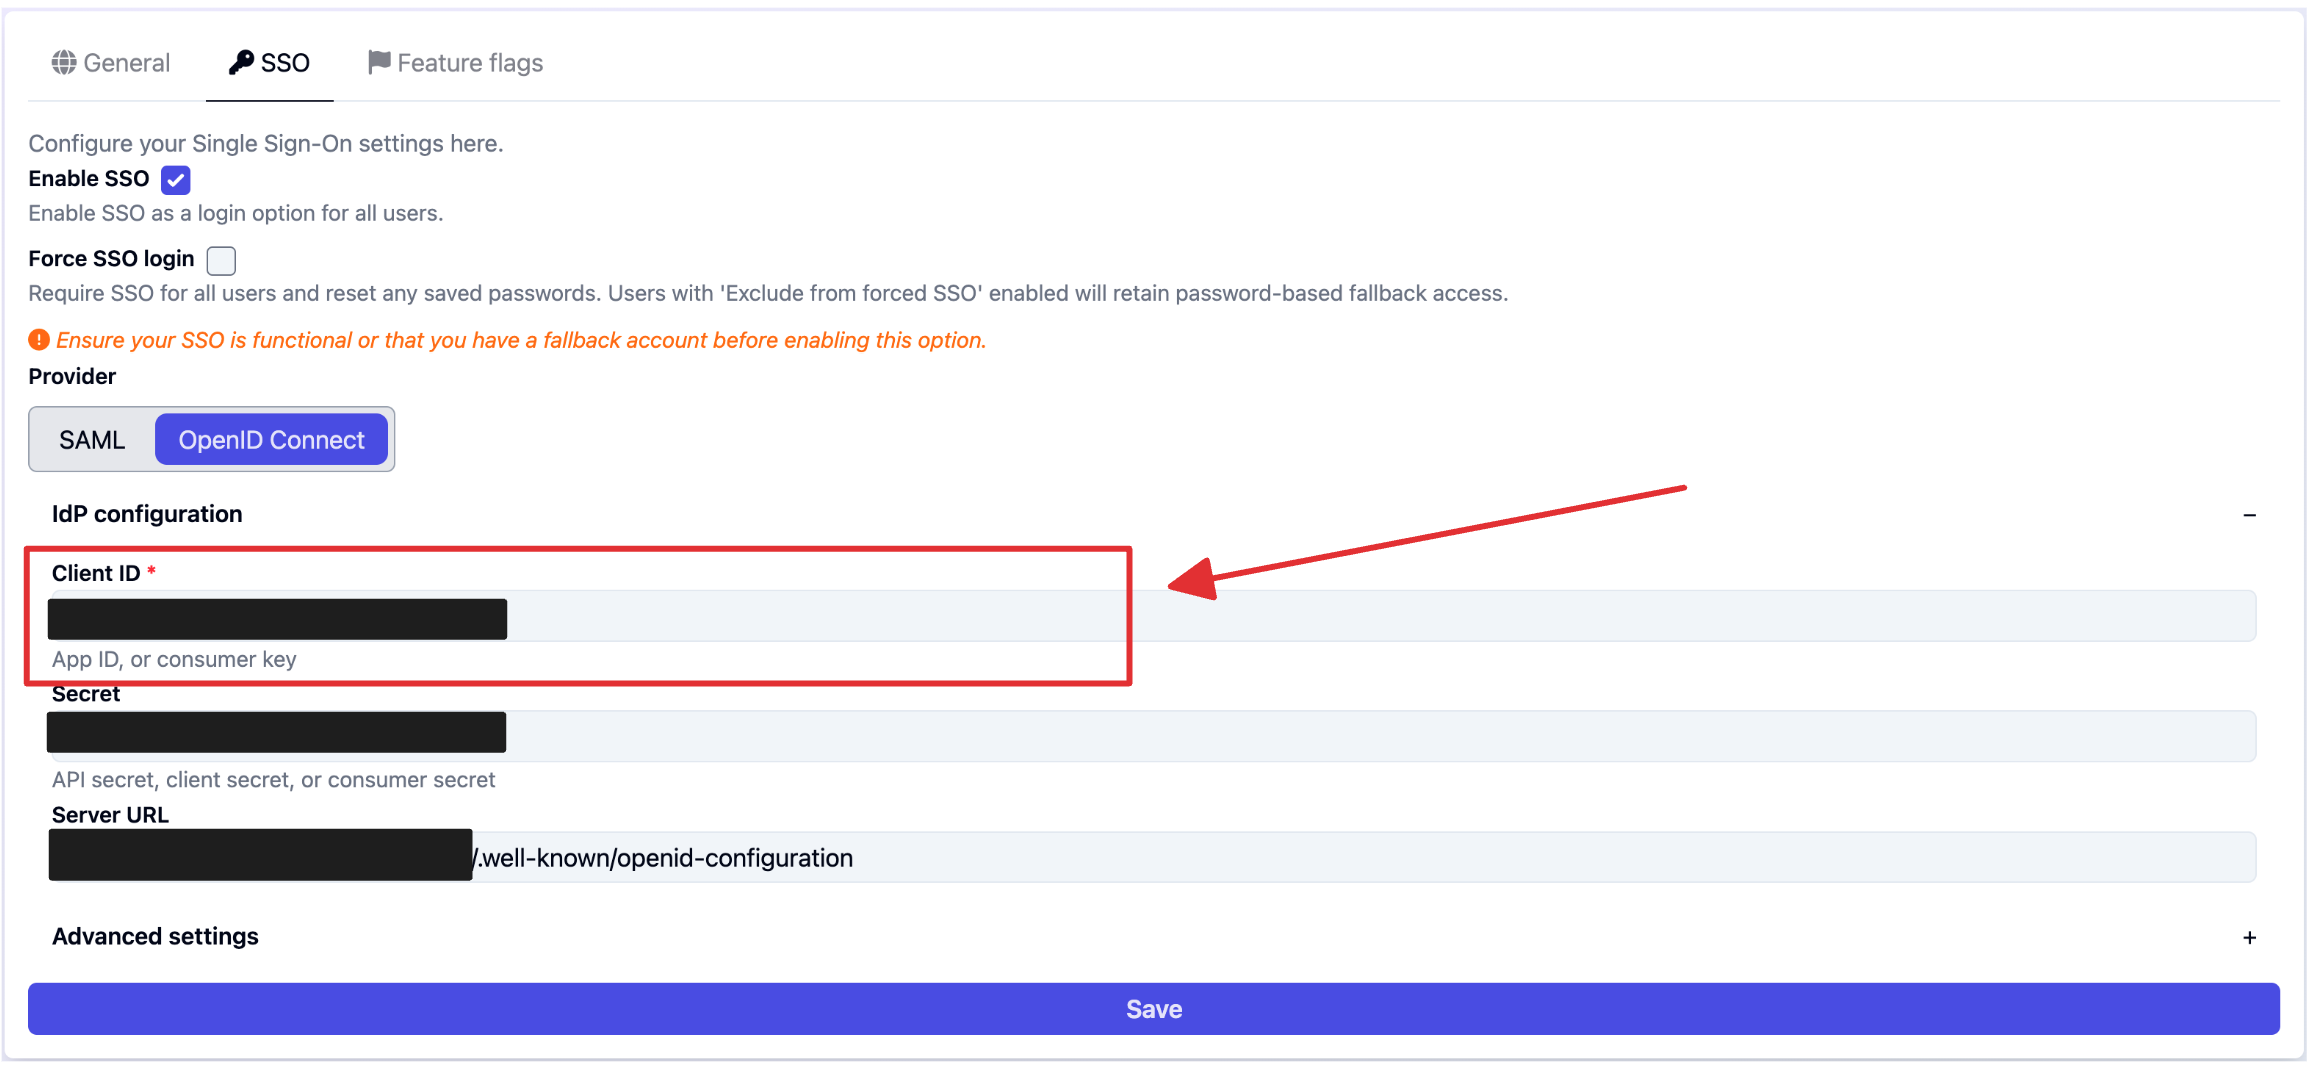
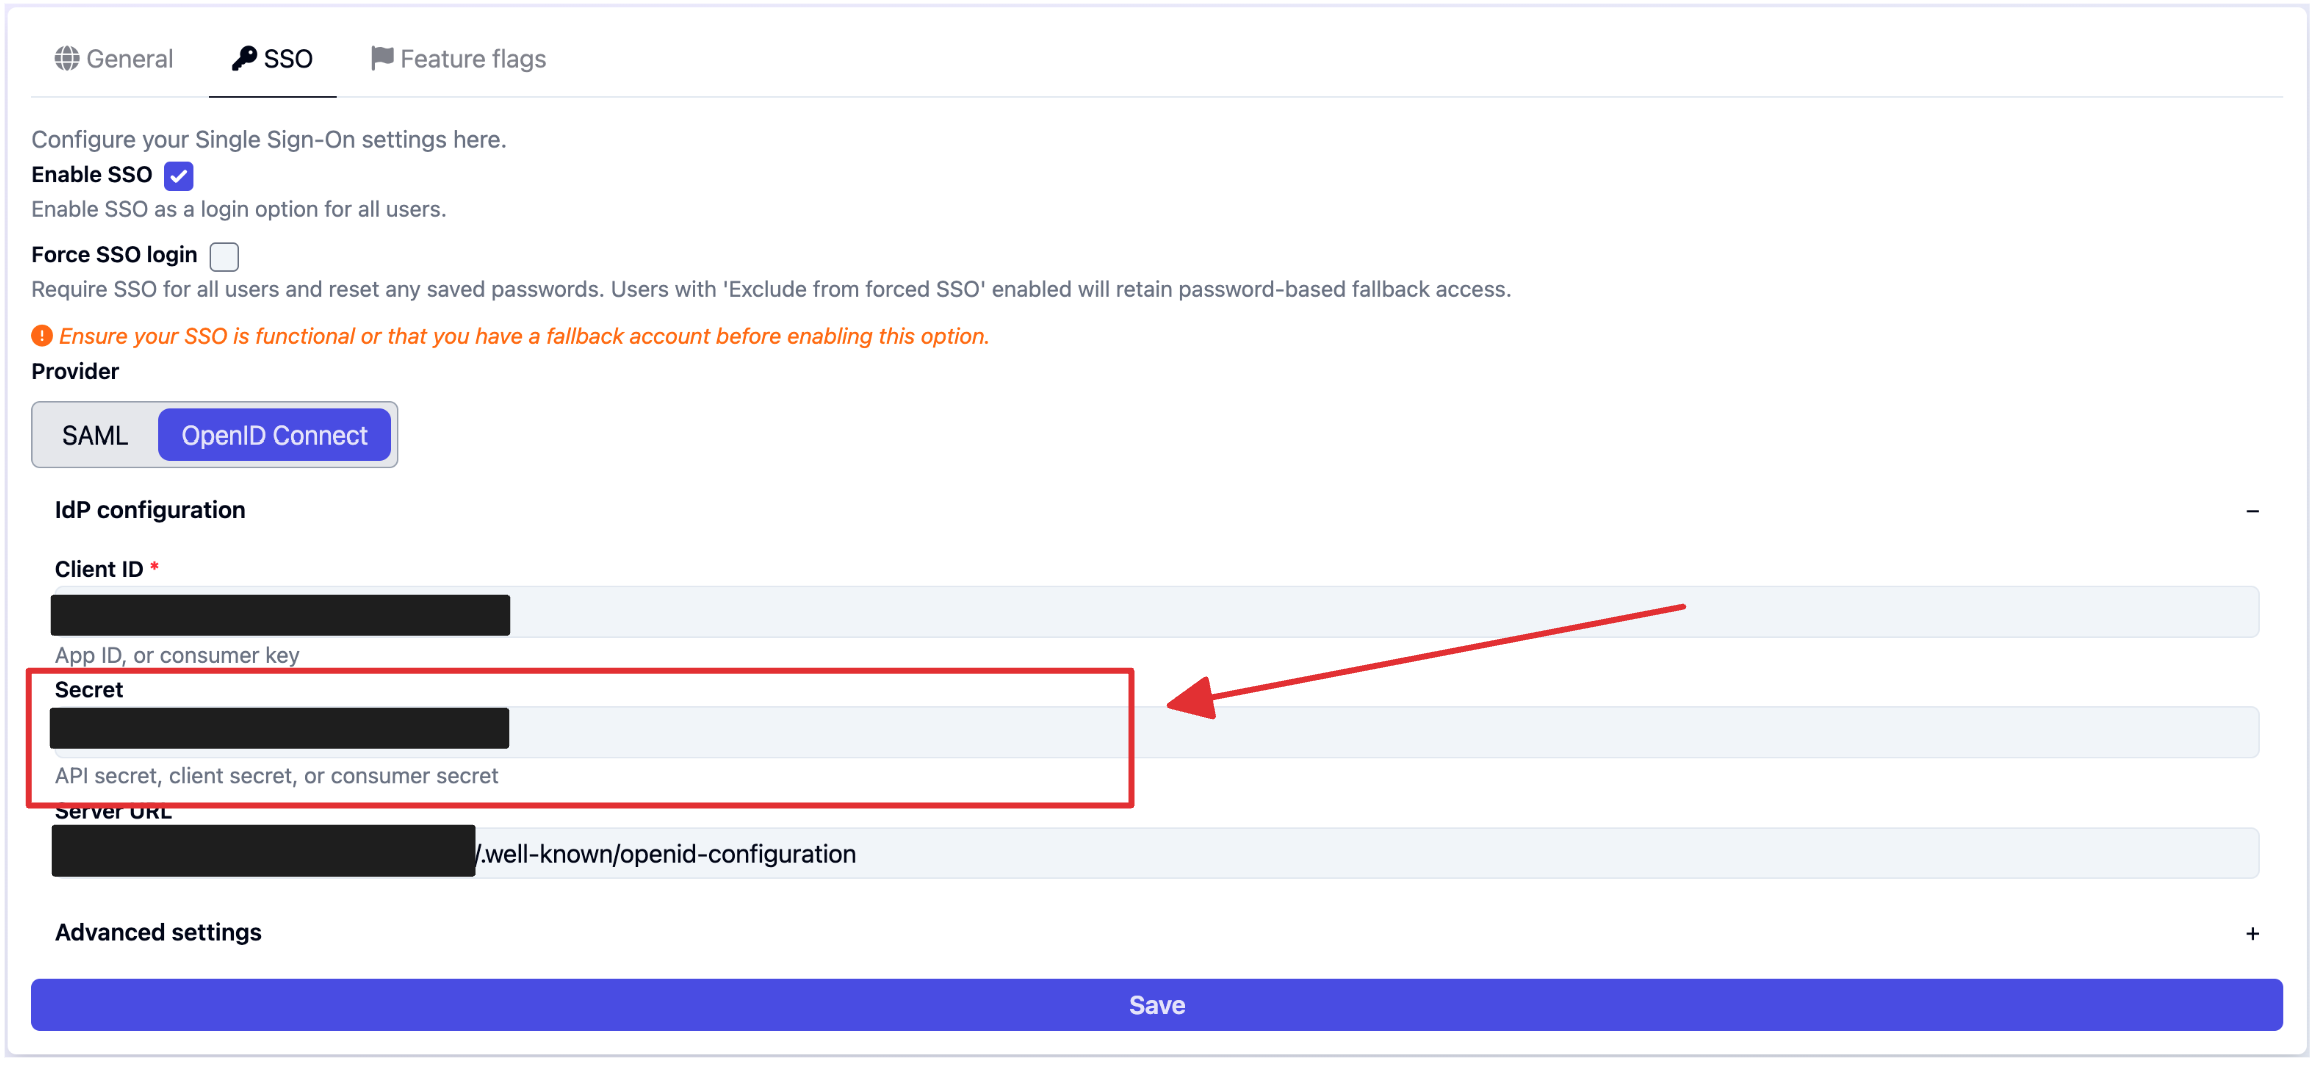
Once you've retrieved the **Client ID**, the **Client Secret** and the **Issuer URL** (sometimes called the discovery or `.well-known` URL) from your provider, the configuration on CISO Assistant is pretty simple.
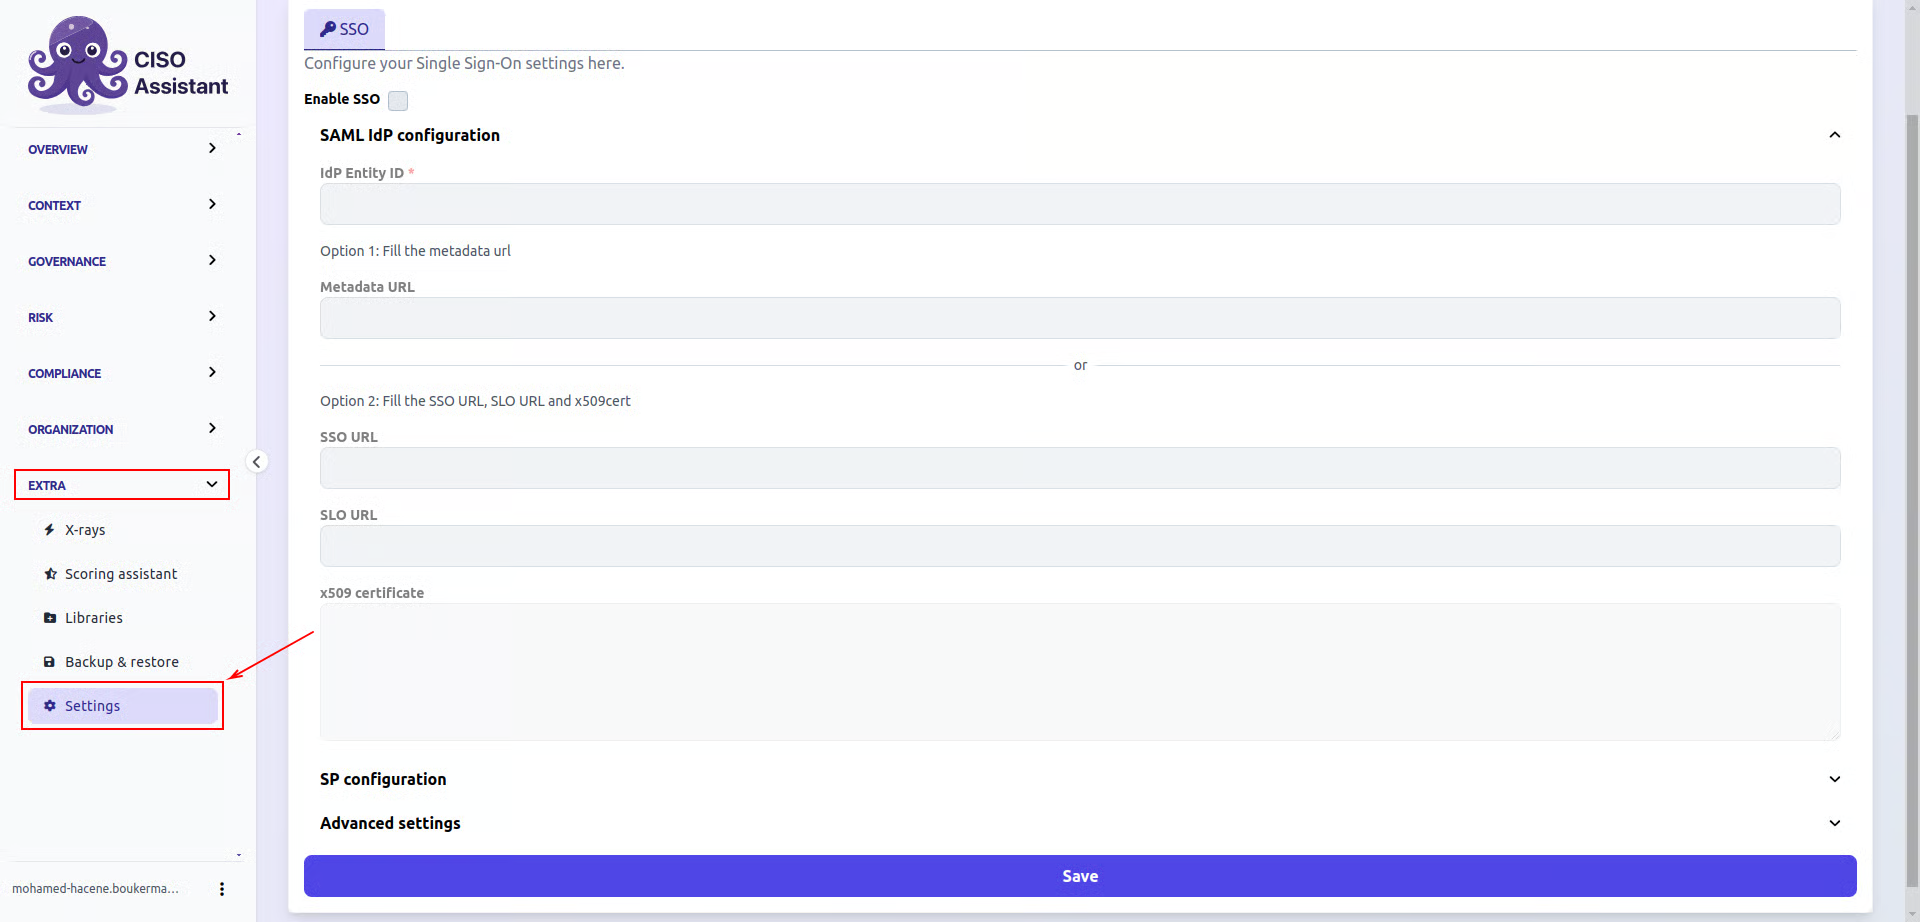
1. Log in into CISO Assistant as an **administrator > Extra > Settings**
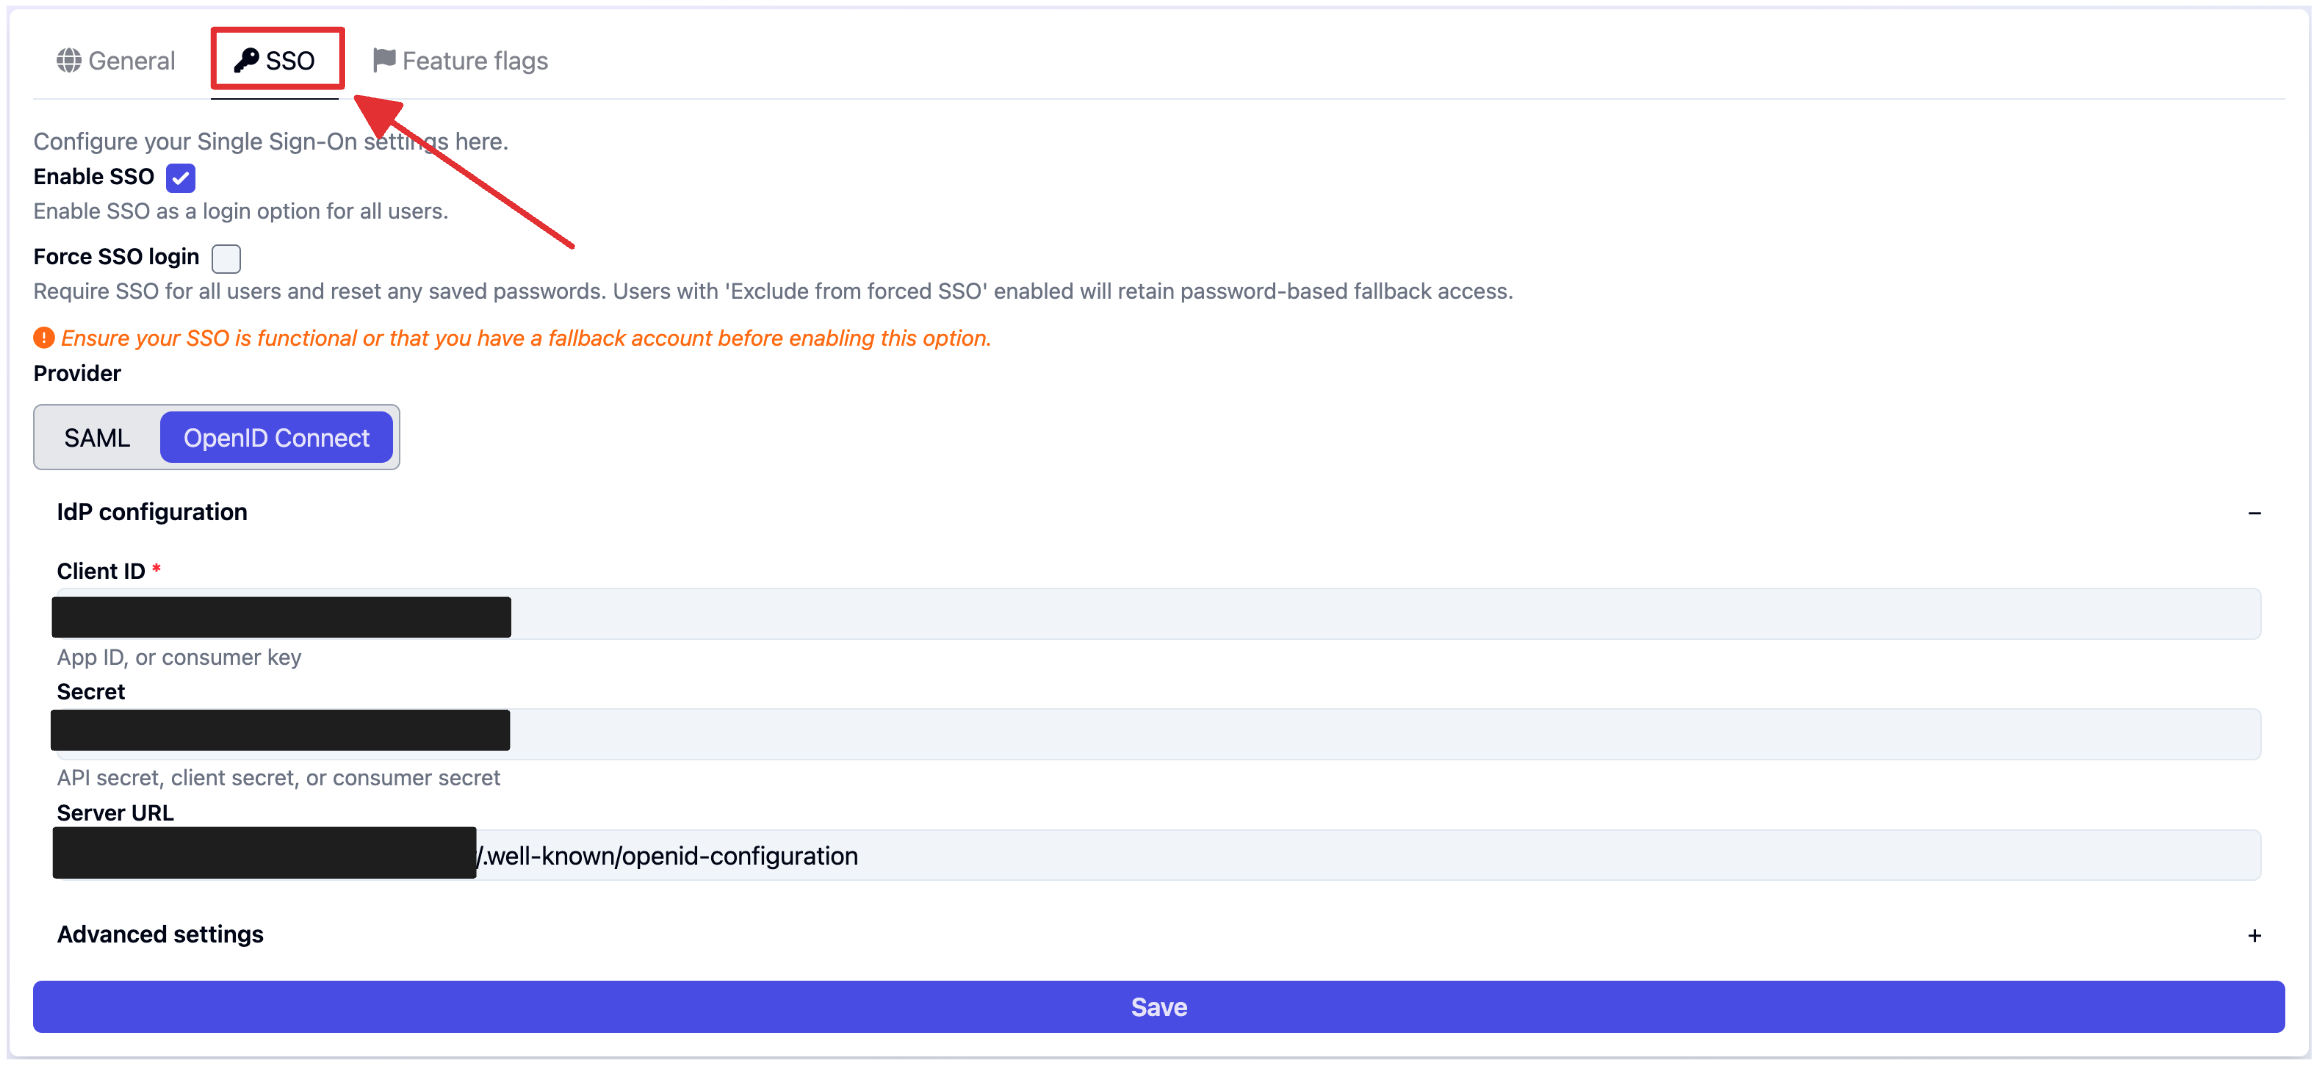
2. Navigate to **SSO** settings
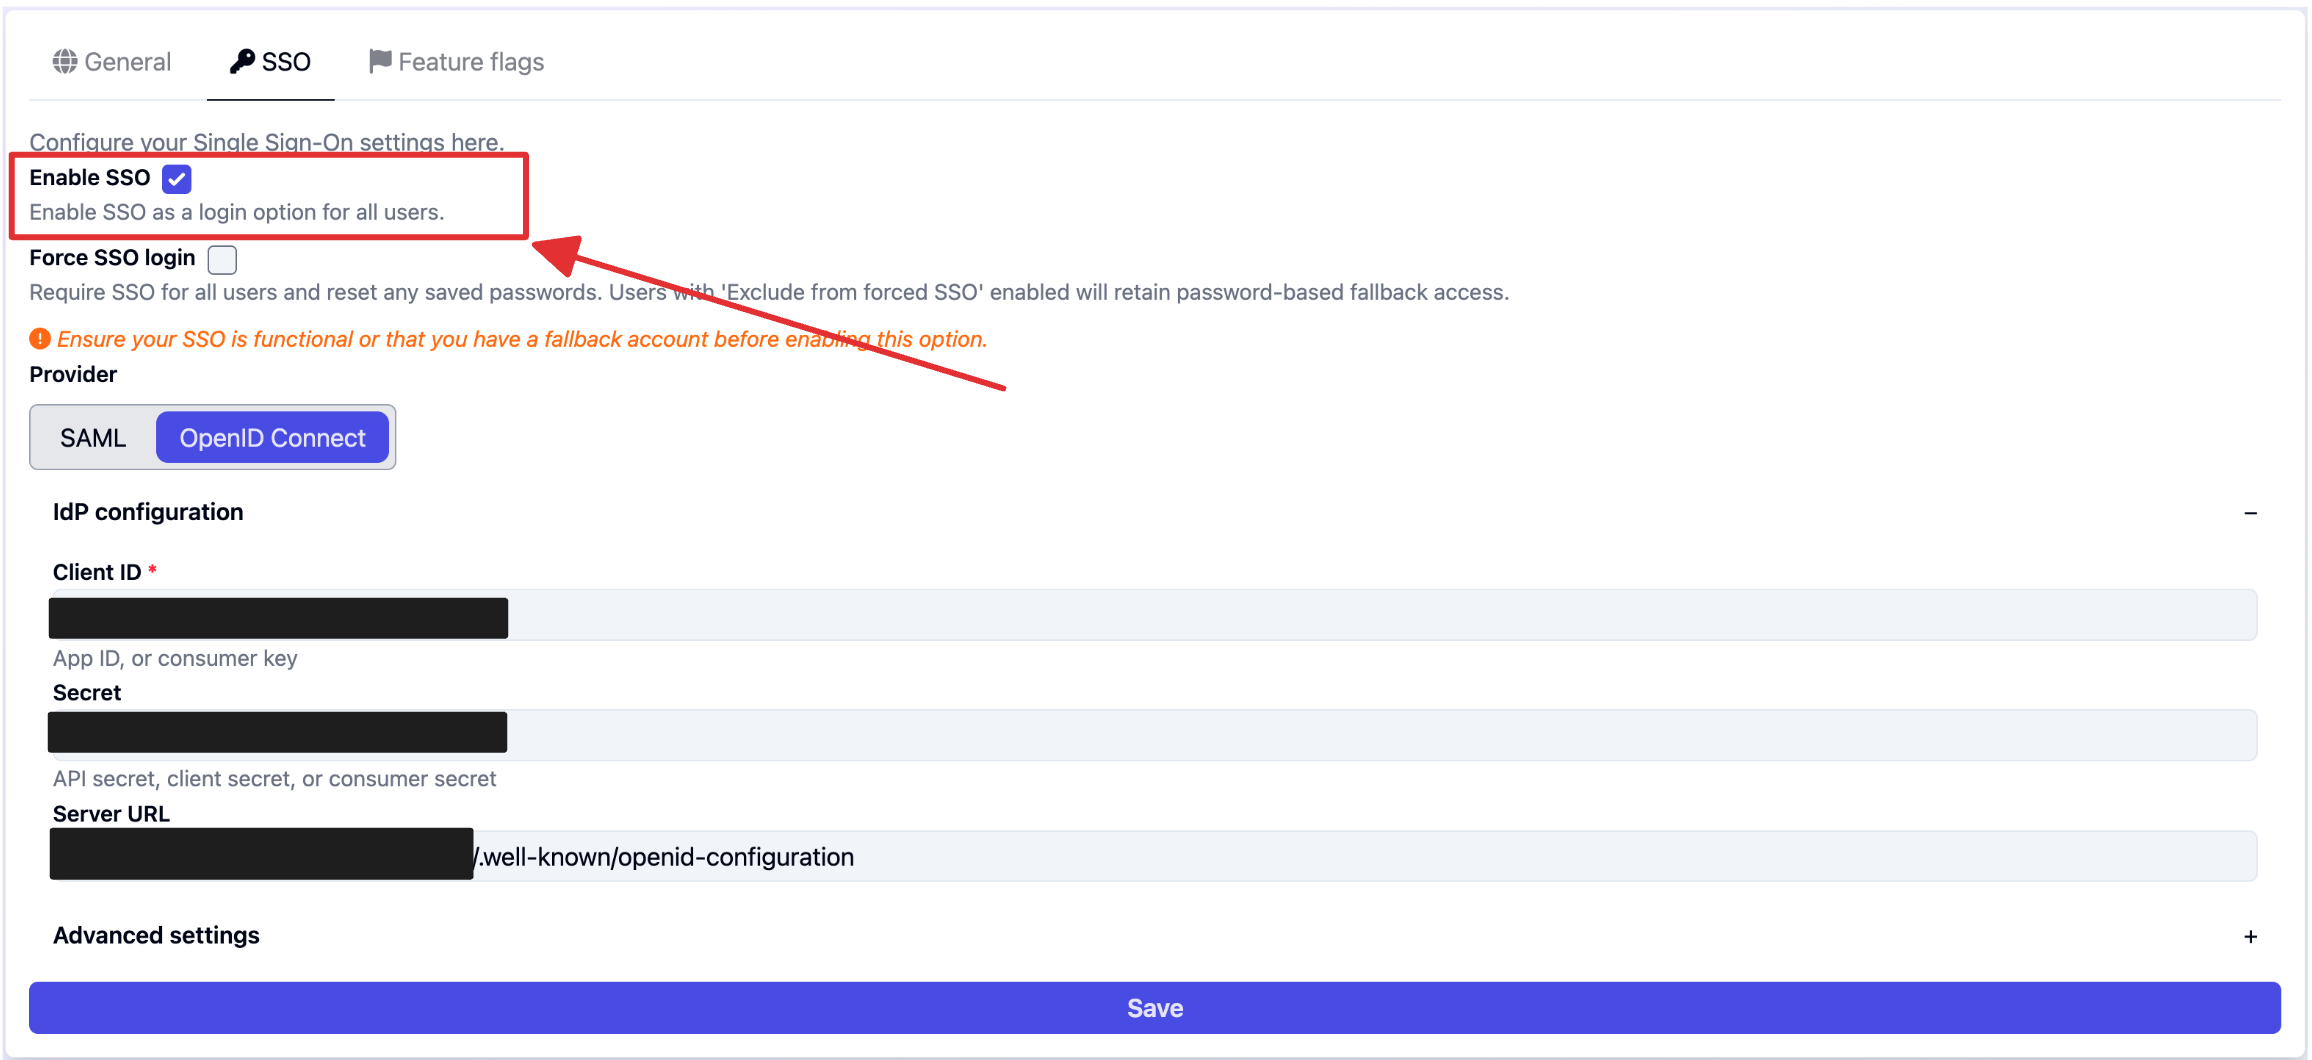
3. **Enable SSO**
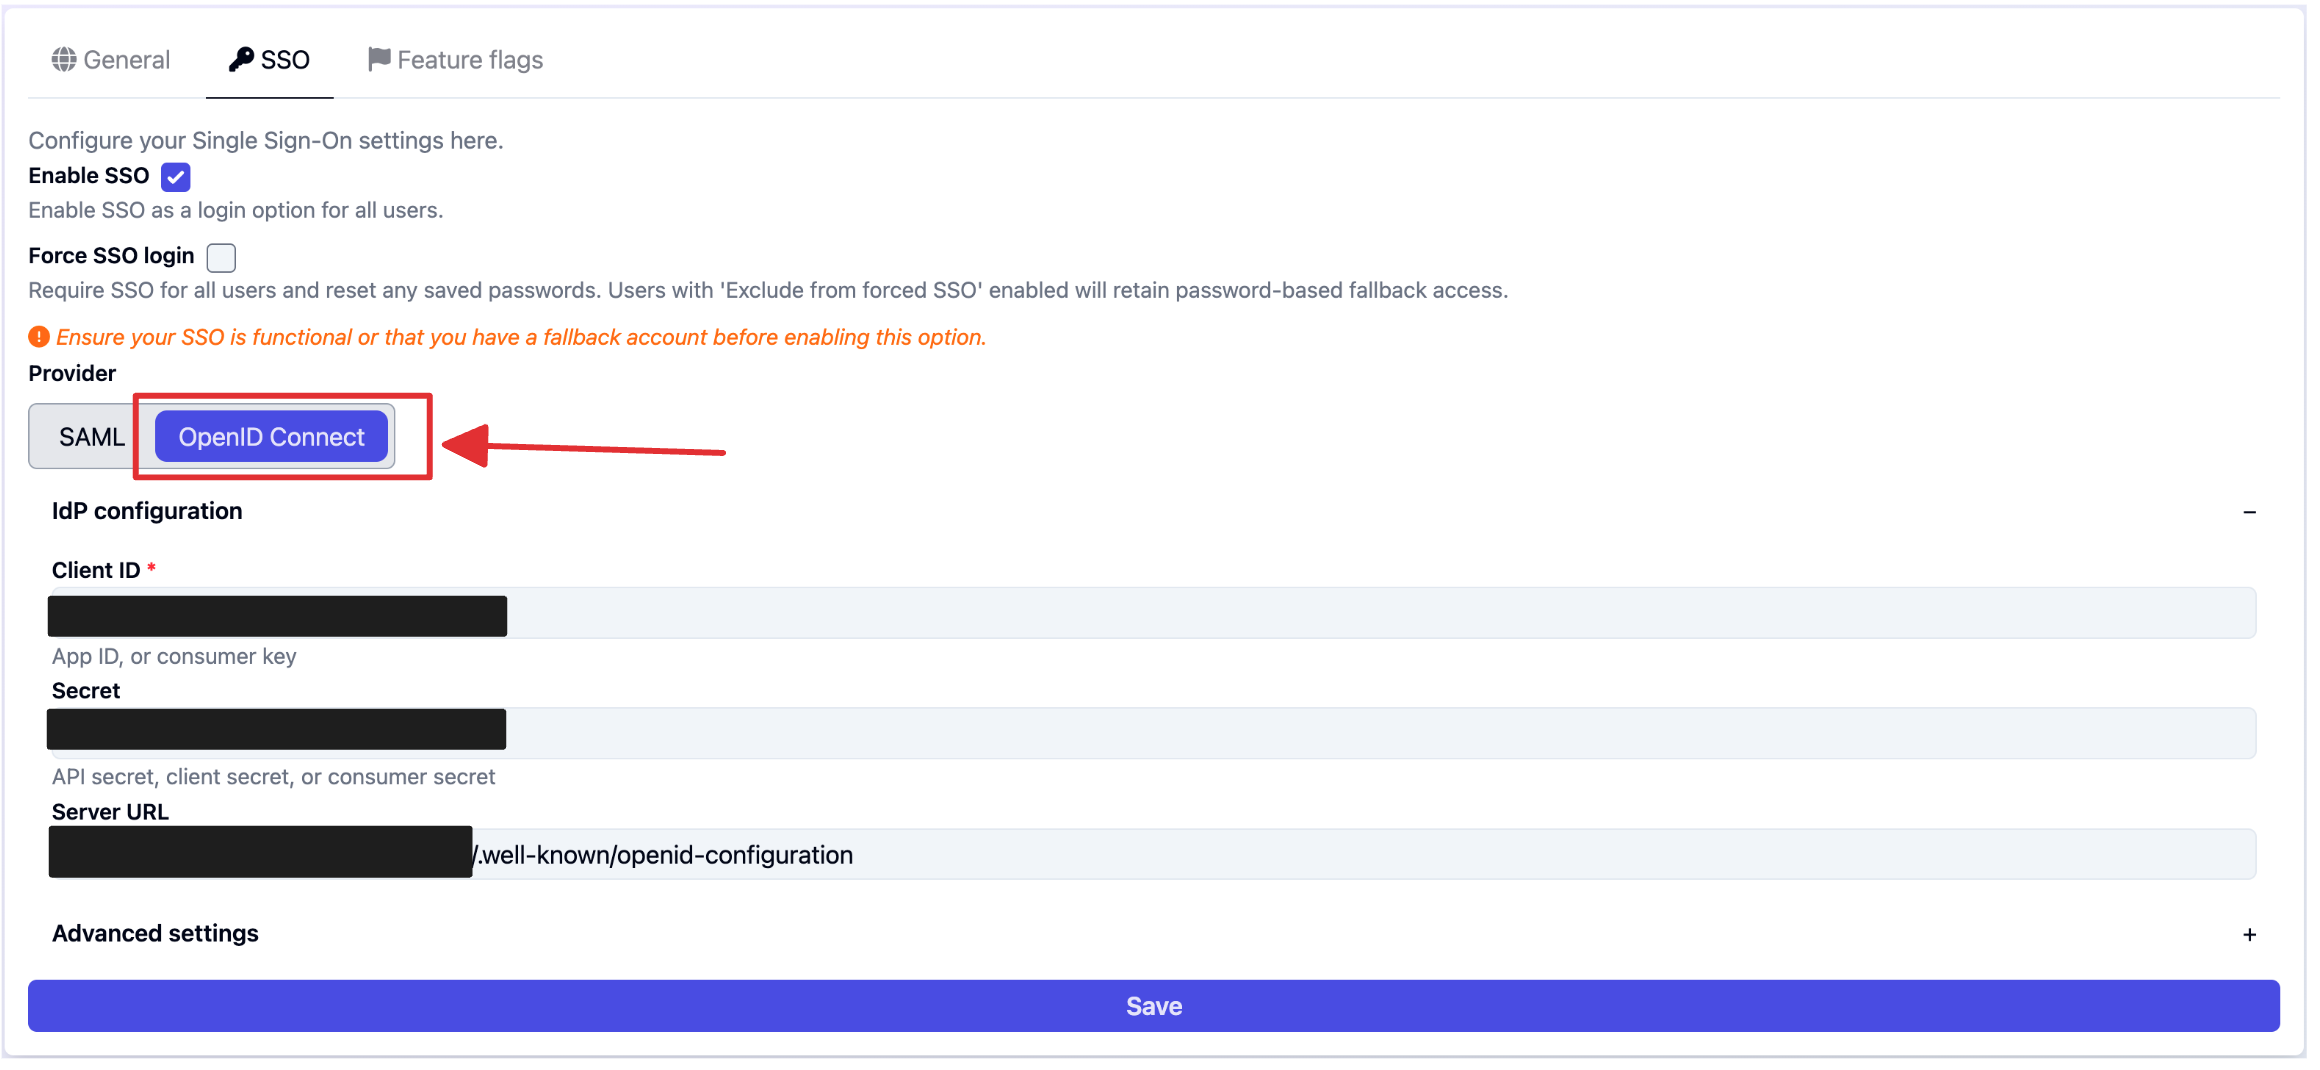
4. Select the **OpenID Connect** provider
5. Enter the **Client ID**
6. Enter the **Client secret**
7. Enter the **Server URL**
8. If your identity provider requires other OAuth scopes, open **Advanced settings** and enter them as a comma-separated list in **Additional scopes**. They are appended to the default `openid`, `profile`, and `email` scopes.
9. And that's it! Don't forget to **click the 'Save' button**
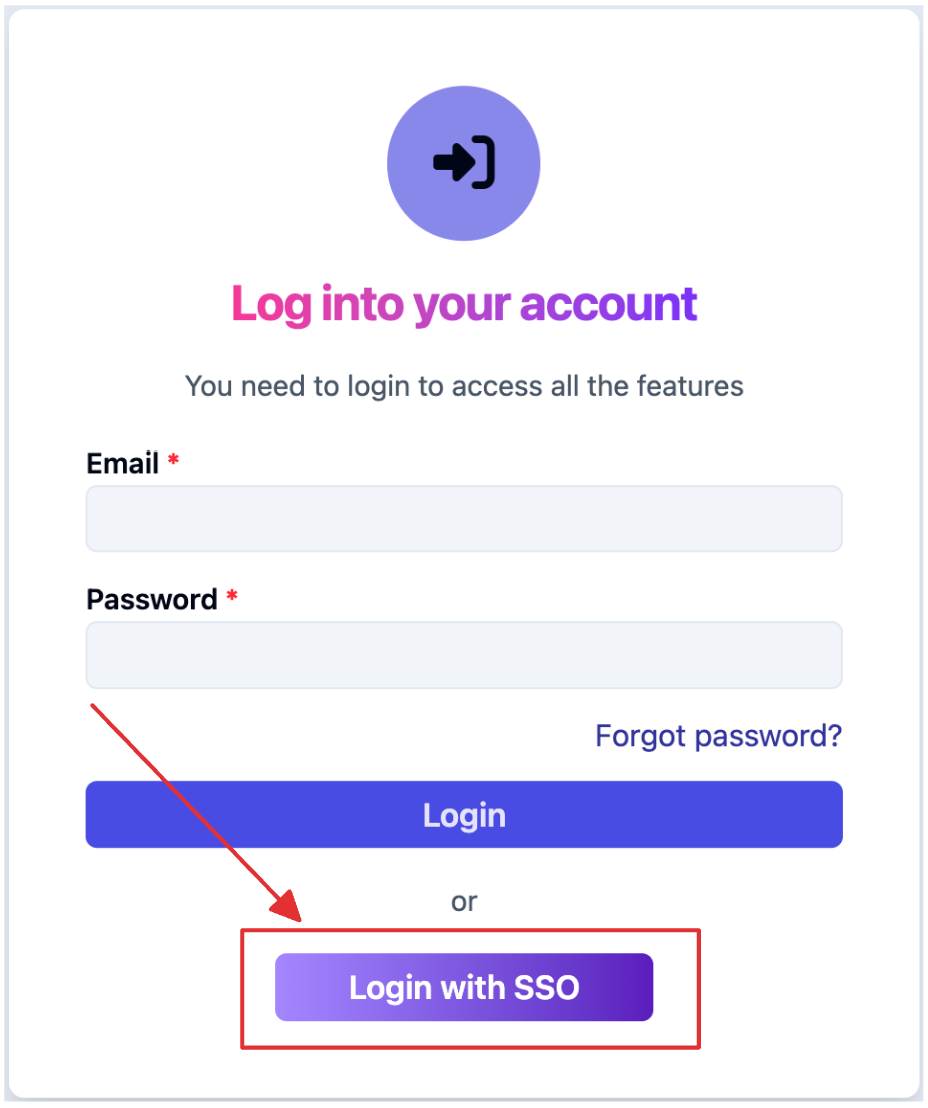
10. You should now be able to see the **Login with SSO** button
{% hint style="warning" %} Be aware that the user needs to be created on CISO Assistant to be authenticated with SSO.
{% endhint %}
{% hint style="info" %}
CISO Assistant automatically sends a standards-compliant `state` and `nonce` on every OIDC authorization request (43 characters matching `^[A-Za-z0-9-._~]{43,128}$`), and validates the `nonce` claim returned in the `id_token`. No configuration is required. This is helpful for identity providers that enforce format or length constraints on these parameters. Per OIDC Core 3.1.3.7, the `nonce` sent in the authorization request must be present and match in the `id_token` — a missing or mismatched nonce will reject the login.
{% endhint %}
### Single Logout
Turn on **Enable service provider-initiated single logout** in the SSO settings to close the OIDC session at the identity provider when users log out of CISO Assistant (see [Single Logout](/ciso-assistant/configuration/sso.md#single-logout) for the general behavior). It additionally requires:
* an `end_session_endpoint` in the provider's OpenID configuration, and
* `/login` registered as an allowed post-logout redirect URI on the OIDC client.
CISO Assistant calls the end-session endpoint with `client_id`, `id_token_hint`, and that post-logout redirect URI.
{% hint style="info" %}
With Microsoft Entra ID, OIDC logout still prompts the user to select an account, because Entra ignores the standard `id_token_hint`. The logout itself works, but the prompt cannot be suppressed without Entra-specific configuration. For a prompt-free single logout with Entra ID, use SAML instead.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://intuitem.gitbook.io/ciso-assistant/configuration/sso/oidc.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.